
Table of Contents
- The Evolution of Digital Forensics Services in Damascus
- Core Disciplines in Enterprise Cyber Investigations
- Comparative Analysis: Commercial vs. Open-Source Forensics Tools
- Modern Methodologies: Memory, Network, and Cloud Forensics
- Building Enterprise Cyber Resilience and Legal Readiness
- Strategic Value of Professional Digital Forensics Services in Damascus
- Frequently Asked Questions
- Modern corporate security requires enterprise-grade digital forensics services in Damascus to defend assets, uncover cyber sabotage, and protect organizational integrity.
- Balancing proprietary forensic suites like EnCase and FTK against robust open-source alternatives like Autopsy offers tailored efficiency across varied enterprise budgets.
- Adherence to chain-of-custody protocols ensures digital evidence retrieved from endpoints, memory, or networks remains admissible and defensible across institutional and legal proceedings.
The Evolution of Digital Forensics Services in Damascus
The modern digital landscape in Syria has witnessed rapid technological integration across financial systems, telecommunications, legal institutions, and private enterprises. With this digital shift comes sophisticated exposure to Advanced Persistent Threats (APTs), corporate data theft, financial fraud, and disruptive malware attacks. Mitigating these systemic operational risks requires deploying comprehensive digital forensics services in Damascus that offer deep evidential discovery, chain-of-custody preservation, and detailed threat intelligence. Modern corporate defense is no longer merely reactive; it demands meticulous forensic telemetry capable of identifying the precise timeline, execution vector, and payload delivery of any unauthorized intrusion.
As organizations upgrade their internal network architectures, enterprise security leads often look toward proven regional methodologies. Engaging expert guidance—such as utilizing advanced support from a digital forensics and incident response provider—helps local enterprises integrate internationally aligned digital investigation frameworks into their threat modeling. In an era where digital evidence dictates corporate liability and shareholder trust, procuring elite digital forensics services in Damascus ensures that proprietary intellectual property, employee records, and operational logs are defended against adversaries seeking illicit network manipulation.
Conducting investigations within complex hybrid enterprise IT environments requires specialized competencies. Forensics engineers must decipher low-level file system metadata, analyze volatile registers, parse distributed ledger transactions, and unravel multi-tiered distributed denial-of-service operations. By relying on industry-grade digital forensics services in Damascus, corporate entities establish an immutable posture that stands firm against regulatory audits, corporate sabotage, and internal threat actors.
Core Disciplines in Enterprise Cyber Investigations
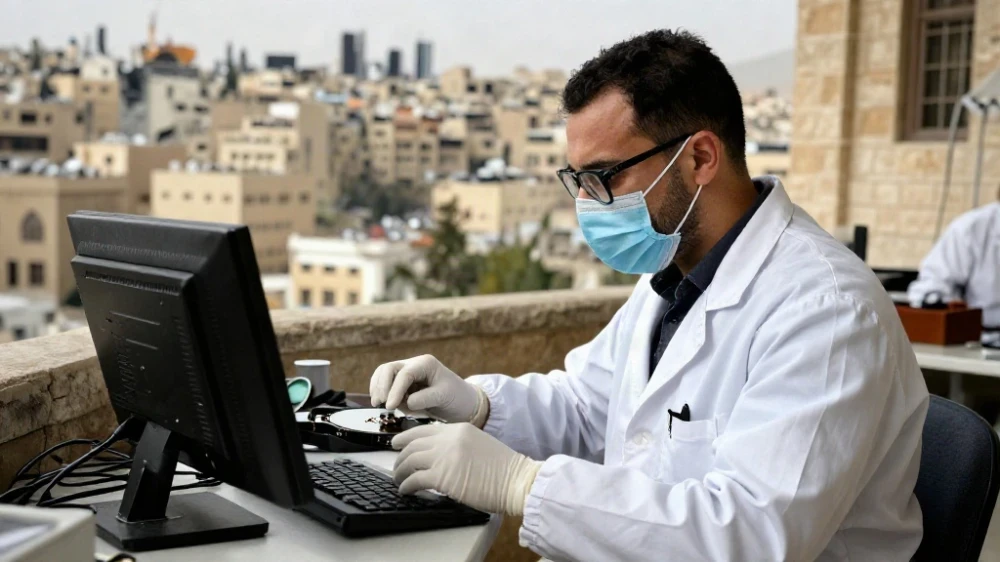
Enterprise forensic engagements require a multidisciplinary approach tailored to the specific nature of each security incident. When organizations encounter breaches, digital forensics services in Damascus operate across several essential domains to reveal the true operational scope of unauthorized network activity.
1. Disk and File System Forensics
Endpoint examination remains a foundational pillar of forensic work. Analysts examine physical and virtual hard disks to reconstruct deleted files, uncover hidden partitions, parse MFT (Master File Table) artifacts, and analyze unallocated clusters. By utilizing bit-stream disk imaging techniques, investigators create exact bit-by-bit duplicates of compromised storage drives. This ensures that the original media remains completely untampered, maintaining evidentiary integrity throughout rigorous investigation cycles.
2. Memory (RAM) Analysis
Modern adversaries frequently execute sophisticated fileless malware campaigns that live entirely within volatile system memory to bypass conventional signature-based antivirus scanners. High-tier digital forensics services in Damascus prioritize immediate physical RAM capture before systems are rebooted. Through deep runtime introspection, specialists extract injected dynamic-link libraries (DLLs), reveal concealed command-line executions, identify active network sockets, and pull decrypted encryption keys directly from volatile memory pools.
3. Network and Perimeter Forensics
Lateral movement across organizational subnets leaves distinct footprints on network switches, perimeter firewalls, proxy appliances, and intrusion detection systems. Correlating full packet captures (PCAP) with continuous NetFlow streams enables analysts to determine the exact origin of a breach, trace data exfiltration routes, and monitor live command-and-control (C2) communication channels. These empirical network insights provide unambiguous timelines necessary to isolate affected enterprise segments.
Understanding these technical processes aligns closely with established scientific guidelines, such as the comprehensive frameworks published by the National Institute of Standards and Technology, which govern incident recovery and evidentiary handling. Implementing these proven international standards through reliable digital forensics services in Damascus allows Syrian institutions to ensure institutional-grade accountability and precise threat attribution.
Comparative Analysis: Commercial vs. Open-Source Forensics Tools
Investigative efficiency depends heavily on the tools, frameworks, and decoders selected by the incident response team. Within the realm of digital forensics services in Damascus, technical teams strategically deploy both commercial enterprise software and robust open-source tools to handle petabyte-scale data acquisitions, forensic indexing, and artifact reconstruction.
| Tool / Platform | Primary Specialty | Key Strengths | Operational Limitations | Ideal Deployment Scenario |
|---|---|---|---|---|
| EnCase Forensics | Disk, File System & Triage | Court-admissible E01 image hashing, comprehensive case indexing, robust scripting (EnScript) | High licensing costs, steep learning curve for junior analysts | Formal litigation, corporate fraud, internal regulatory compliance |
| Autopsy / The Sleuth Kit | Open-Source Disk Forensics | Modular architecture, zero licensing overhead, native keyword search, web artifact extraction | Slower processing speeds on massive, multi-terabyte unallocated storage spaces | Budget-conscious corporate audits, rapid incident triage, research labs |
| Volatility Framework | Volatile Memory (RAM) Forensics | Superior extraction of stealth rootkits, process hollowing detection, multi-OS kernel support | Strict Command Line Interface (CLI), requires custom symbol tables for newer OS kernels | Detecting advanced fileless malware, zero-day analysis, APT tracking |
| FTK (Forensic Toolkit) | Distributed Enterprise Analysis | Oracle-backed database indexing, rapid search clustering, high-throughput email parsing | Resource-intensive infrastructure demands, complex backend administration | Large-scale corporate investigations involving thousands of corporate endpoints |
| Wireshark & Zeek | Network Protocol Forensics | Deep protocol decoding, programmatic network logging, behavioral anomaly detection | High storage consumption for raw PCAPs, requires high analyst domain knowledge | Investigating data exfiltration, unauthorized pivot attempts, C2 traffic tracking |
Deploying the right combination of these advanced platforms requires deep domain specialization. Expert digital forensics services in Damascus leverage the strengths of each platform—using FTK and EnCase for immutable corporate file system audits, while running Volatility and Zeek to untangle runtime intrusions. This hybrid approach enables organizations to optimize processing costs while securing thorough forensic results.
Modern Methodologies: Memory, Network, and Cloud Forensics
Executing forensically sound investigations requires strict adherence to standardized incident response workflows. Professional digital forensics services in Damascus rely on repeatable, scientifically validated methodologies to transition seamlessly from the initial detection phase to evidence extraction, deep analysis, and executive reporting.
Phase 1: Identification and Secure Evidence Preservation
The moment a security anomaly is flagged, whether an active ransomware payload or an unauthenticated administrative escalation, forensic integrity must be prioritized. First responders secure volatile evidence before pulling physical power cords or re-imaging operating systems. By utilizing hardware write-blockers, forensic specialists create bit-stream copies of physical disks, compute cryptographically secure SHA-256 and MD5 hash values, and document every step on formal chain-of-custody ledgers.
Phase 2: Comprehensive Artifact Extraction and Reverse Engineering
Once raw images are secured, specialized digital forensics services in Damascus parse low-level operational artifacts, including:
- Prefetch Files and Amcache.hve: Providing concrete evidence of program execution, original file directories, and system runtime contexts.
- Windows Event Logs: Analyzing Event IDs (such as 4624 for successful logons, 4672 for special privileges, and 7045 for service installation) to isolate lateral movement.
- Shimcache (AppCompatCache): Identifying historical malware execution traces across application compatibility databases.
- Web and Cloud Telemetry: Correlating session tokens, cloud storage synchronization activity, and external IP access records.
Phase 3: Threat Actor Timeline Reconstruction
By synchronizing endpoint system events, network firewall sessions, and Active Directory logs into a unified timeline, analysts construct a comprehensive account of adversary activity. This holistic timeline demonstrates how an attacker penetrated the perimeter, escalated user privileges, disabled corporate security controls, and accessed sensitive databases. Accessing these analytical capabilities through dependable digital forensics services in Damascus equips executive teams with clear, defensible facts rather than unverified technical hypotheses.
Building Enterprise Cyber Resilience and Legal Readiness
Modern organizations in Damascus must prepare for complex cyber challenges before a security breach occurs. Developing robust forensic readiness allows businesses to minimize business downtime, limit regulatory exposure, and accelerate digital investigations. Effective forensic preparedness requires seamless collaboration across internal IT units, legal counsel, and executive teams.
Organizations prioritizing proactive digital forensics services in Damascus typically maintain continuous centralized log collection architectures. By directing endpoint detection logs, domain controller authentication events, and network flow telemetry into secure, write-once-read-many (WORM) storage environments, security teams prevent sophisticated adversaries from clearing event logs to cover their tracks. When an incident occurs, analysts can immediately access authentic, unmanipulated event streams.
Furthermore, internal threat mitigation requires clear protocols for handling employee misconduct, IP theft, and corporate fraud. Establishing enterprise-wide guidelines for device preservation, system monitoring, and credential segregation ensures internal reviews align with international operational standards. Partnering with seasoned providers of digital forensics services in Damascus enables businesses to conduct discreet internal investigations that protect brand reputation and maintain workplace integrity.
Strategic Value of Professional Digital Forensics Services in Damascus
Navigating cybersecurity threats in 2026 requires specialized expertise that goes beyond routine antivirus monitoring and basic firewall administration. Corporate leadership requires deep visibility into operational vulnerabilities, root causes of system failures, and accurate risk assessments. Engaging dedicated provides organizations with decisive strategic advantages:
- Rapid Incident Containment: Immediately identifying patient zero and severing malicious command-and-control channels prevents malware outbreaks from turning into catastrophic operational shutdowns.
- Court-Admissible Evidence Packaging: Adhering to rigorous chain-of-custody protocols ensures all recovered artifacts, timeline visualizations, and forensic reports can withstand rigorous scrutiny in formal commercial dispute proceedings.
- Protection Against Insider Threats: Detecting unauthorized data transfers, privileged credential sharing, and covert data exfiltration helps safeguard mission-critical intellectual property and confidential customer records.
- Hardened Post-Breach Remediation: Root-cause analysis provides engineering teams with practical remediation plans, preventing adversaries from exploiting identical architectural vulnerabilities in the future.
Investing in advanced transforms incident response from a reactive disruption into a controlled, strategic enterprise capability. By aligning advanced forensic tools, sound scientific methodologies, and seasoned cyber expertise, Syrian enterprises can confidently defend their digital infrastructure against today’s sophisticated cyber adversaries.
Frequently Asked Questions
What is the primary difference between commercial and open-source forensic tools?
Commercial forensic tools such as EnCase and FTK provide automated artifact parsing, integrated database management, and streamlined workflows tailored for complex corporate litigation. In contrast, open-source utilities like Autopsy and Volatility offer powerful command-line control and modular adaptability without expensive licensing costs. Professional often integrate both approaches to achieve maximum investigative coverage.
How does preserving the chain of custody affect corporate investigations?
The chain of custody documents every individual who collected, handled, transferred, and analyzed a piece of digital evidence. Maintaining strict chain-of-custody documentation, supported by cryptographic hashing (SHA-256), proves that disk images and system logs have remained entirely unaltered. This level of verification is essential for presenting evidence in internal disciplinary hearings, regulatory audits, or formal legal disputes.
Why is volatile memory (RAM) analysis critical during a cyber incident?
Many modern cyber intrusions utilize in-memory execution, process injection, and fileless malware techniques that leave zero traces on permanent physical hard drives. Capturing and analyzing volatile RAM preserves active network connections, decrypted encryption keys, running processes, and injected malicious code that disappear completely once an infected endpoint is restarted or powered down.



